Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation – Krebs on Security

The recent arrest of 24-year-old Dutch national Pepijn van der Stap has sent shockwaves through the international cybersecurity landscape, triggering a volatile escalation in retaliatory cyberattacks. Van der Stap, a former software engineer and security volunteer who once operated under the alias "Umbreon," was apprehended by Dutch authorities on September 16, 2026, on suspicion of facilitating extensive data theft and extortion schemes for the notorious hacker collective ShinyHunters. His detention has not only dismantled a key node in the group’s operations but has also unveiled a complex, multi-layered power struggle occurring within the highest echelons of modern cybercriminal organizations.
The arrest occurred against a backdrop of heightened scrutiny by the Dutch police, who have been actively seeking to identify the voice behind a February 2026 social engineering attack against Odido, the Netherlands’ largest mobile telecommunications provider. That breach resulted in the unauthorized exfiltration of personal data belonging to 6.2 million Dutch citizens. Following Van der Stap’s capture, the remaining members of ShinyHunters abandoned their previously calculated operational style, launching a series of high-profile, brazen assaults, most notably against the Federal Bureau of Investigation (FBI).
A Dual Identity Unmasked
The profile of Pepijn van der Stap presents a classic "Dr. Jekyll and Mr. Hyde" archetype. A resident of Almere and Lelystad, Van der Stap previously garnered headlines in 2023 following a conviction related to a massive string of data thefts and extortion campaigns that yielded illicit profits estimated between €1.5 million and €2.7 million. During his trial, he admitted to operating under the "Umbreon" handle, a moniker inspired by the Pokémon character, which he used to peddle stolen databases on underground forums such as RaidForums and Breached.

Despite this criminal activity, Van der Stap maintained a legitimate professional facade. By day, he worked as a software engineer for the Amsterdam-based cybersecurity startup Hadrian and contributed his skills to the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit organization focused on ethical security research. Following his 2023 conviction, he was sentenced to four years in prison, with one year suspended. He was released in December 2025, claiming in subsequent interviews to be a reformed individual dedicated to making amends for his past transgressions. At the time of his most recent arrest, he was employed as an offensive security lead at Neo Security.
The Escalation: From Data Theft to Global Provocation
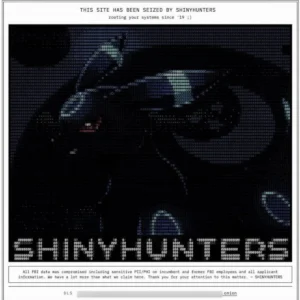
The immediate aftermath of Van der Stap’s arrest saw a dramatic shift in the tactics employed by ShinyHunters. Within days, the group claimed responsibility for a breach of the FBI’s recruitment portal, apply.fbijobs.gov. The breach exposed sensitive personal identifiable information (PII) of over 5,000 FBI employees, including special agents, threat intake examiners, and personnel assigned to the bureau’s major cybercrimes units. Reports from 404 Media and Reuters confirmed that the stolen data included psychiatric and medical records, creating a significant security vulnerability for those tasked with investigating foreign state-backed threats.
Analysts suggest this escalation was driven by a new, more aggressive leadership faction within the group. Intelligence sources indicate that a teenage hacker from Amman, Jordan, known as "Rey," has ascended to a leadership position within a conglomerate known as ScatteredLapsussHunters (SLSH)—an entity formed from the remnants of Scattered Spider, LAPSUS$, and ShinyHunters. The animosity between Rey and Van der Stap appears to be rooted in a power struggle over control of the ShinyHunters brand and the monetization of stolen credentials. The inclusion of "Umbreon" iconography in the FBI site defacement is widely viewed by security researchers as a deliberate attempt by the new leadership to frame the incarcerated Dutchman for the high-stakes breach.
Technical Exploitation and Systemic Risks
The technical sophistication of these attacks has been linked to the exploitation of a vulnerability in Oracle’s PeopleSoft platform (CVE-2026-35273). While Oracle issued a patch for the flaw, ShinyHunters effectively utilized a URL-encoding technique to bypass web application firewall (WAF) mitigations suggested by Mandiant. Google Threat Intelligence Group (GTIG) and Mandiant have confirmed that the group used this vulnerability to conduct mass-exploitation campaigns across multiple sectors, including healthcare, agriculture, and transportation.

This campaign highlights the persistent risk posed by supply-chain vulnerabilities in enterprise resource planning (ERP) software. The ability of a single hacking collective to pivot from targeting individual databases to compromising federal agencies demonstrates a concerning maturation of their tactical capabilities. Industry experts estimate that, if left unchecked, ShinyHunters could reach $100 million in illicit extortion revenue for the 2026 fiscal year.
Official Responses and the Pursuit of Justice
The international response to these developments has been swift. On September 29, 2026, the Dutch news outlet RTL reported that investigators have expanded their inquiry to include allegations that Van der Stap may have orchestrated at least two murders, an escalation that elevates the investigation from cybercrime to capital-level offenses.
In the United States, the FBI has taken a public stance, with Brett Leatherman, assistant director of the FBI’s Cyber Division, releasing a video statement. Leatherman thanked Dutch law enforcement for their cooperation and extended a pointed warning to the remaining members of the ShinyHunters collective: "Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left. The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you."
Broader Implications for Cybersecurity
The case of Pepijn van der Stap underscores the inherent difficulty in vetting personnel within the cybersecurity industry, where the line between "offensive security" expertise and criminal intent can often blur. Organizations that employ former hackers as penetration testers or security leads face the ongoing challenge of monitoring for recidivism, especially when psychological triggers or financial pressures remain unaddressed.

Furthermore, the emergence of hybrid cybercrime groups like SLSH indicates that the landscape is moving away from loosely affiliated hacking gangs toward more centralized, operationally diverse criminal enterprises. These groups are increasingly willing to target state infrastructure to create leverage in their extortion negotiations. The "burned" credentials resulting from the infiltration of groups like TeamPCP by security firms have likely fueled a cycle of desperation, causing groups to burn bridges and act with greater volatility.
As the Dutch judiciary prepares to hear the case against Van der Stap on September 29, the global cybersecurity community remains on high alert. The incident serves as a stark reminder that the digital infrastructure governing national security and personal privacy remains vulnerable to the shifting alliances and internal power plays of those who operate in the shadows of the dark web. The collaboration between the FBI and Dutch authorities may signify a new model for cross-border cybercrime investigation, but the challenge of neutralizing groups like ShinyHunters—which have demonstrated both a willingness to innovate and a disregard for international norms—remains a daunting task for law enforcement agencies worldwide.