Critical Security Vulnerabilities in Citrix NetScaler Appliances Trigger Widespread Global Exploitation Campaign

Unknown threat actors are currently orchestrating a sophisticated, large-scale cyberattack targeting Citrix NetScaler ADC and NetScaler Gateway appliances, leveraging a critical memory overflow vulnerability to gain root-level access to sensitive enterprise and government networks across North America and Europe. The campaign, which gained significant momentum in late September 2026, represents a major escalation in the targeting of edge infrastructure, bypassing traditional perimeter defenses to establish persistent, stealthy footholds within high-value target environments.
Security researchers from Mandiant Consulting and the Google Threat Intelligence Group (GTIG) first identified the malicious activity in early September. The threat actors are specifically exploiting CVE-2026-88772, a severe vulnerability with a CVSS score of 9.5, which allows for unauthorized remote code execution. This flaw resides within the Datagram Transport Layer Security (DTLS) protocol handling, a component of the NetScaler Packet Processing Engine (NSPPE). By transmitting malformed or fragmented record headers during the pre-authentication cryptographic handshake, attackers induce heap memory boundary corruption. This corruption diverts the system’s control flow, enabling the execution of arbitrary shellcode with elevated root privileges on the underlying FreeBSD-based operating system.
A Chronology of the Campaign
The timeline of this exploitation surge indicates a rapid evolution from initial discovery to widespread, automated abuse. While limited reconnaissance activity was noted in early September, the situation deteriorated significantly on September 28, 2026. Data from the security firm GreyNoise indicates that around 8:30 a.m. EDT on that date, a wave of mass reconnaissance began, scanning for vulnerable NetScaler instances. By 10:30 p.m. EDT that same day, the activity shifted from simple probing to full-scale, weaponized exploitation.
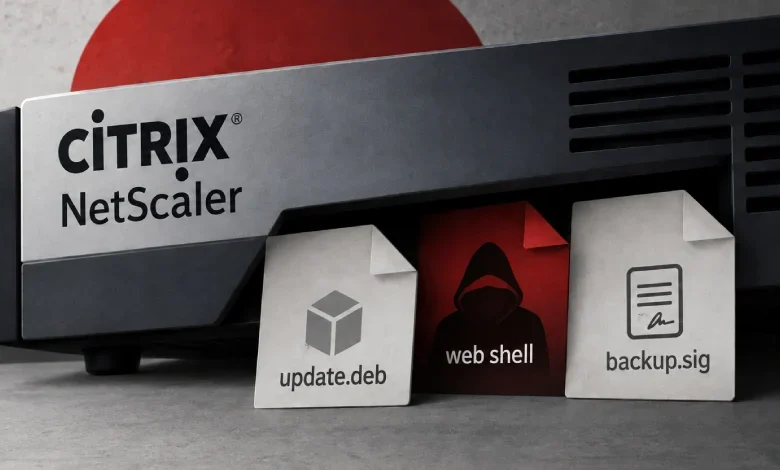
Security analysts observed that once an attacker successfully triggers the heap overflow, they immediately move to install a sophisticated post-exploitation toolkit. The process is highly automated, beginning with the modification of the appliance’s httpd.conf files. This configuration change is designed to instruct the web server to interpret unconventional file types—specifically Debian package format (.deb) files and signature (.sig) files—as executable PHP scripts. This maneuver provides a deceptive, camouflage-based environment for the subsequent deployment of custom malware.

Advanced Malware: WHIPSHOT and SLAPSHOT
The primary tools utilized in this campaign demonstrate a high degree of technical refinement. The researchers identified two distinct components: a web shell known as WHIPSHOT and a companion Python-based tunneler dubbed SLAPSHOT.
WHIPSHOT is a lightweight, highly effective PHP web shell that facilitates remote command execution. Its primary function is to act as a listener, parsing Base64-encoded commands hidden within native HTTP headers. By embedding instructions inside the header of a standard HTTP request, the attackers effectively mask their command-and-control (C2) traffic from traditional signature-based detection systems. When the web shell receives these headers, it decodes the payload, executes the command, and returns the result, all while maintaining minimal disk footprint.
Complementing this is SLAPSHOT, a Python-based utility designed to function as an internal network bridge. Once the initial shell is established, the attackers use SLAPSHOT to proxy traffic into the victim’s internal network. This allows for lateral movement, where the threat actor can conduct reconnaissance, scan internal segments, and harvest credentials from systems that are otherwise shielded from direct external access. In at least one observed case, attackers used this tunnel to manually traverse the internal environment, demonstrating an intent beyond simple data theft—likely aiming for long-term intelligence gathering or ransomware deployment.
Deceptive Persistence and Evasion Tactics
One of the most concerning aspects of this campaign is the sophisticated method used to ensure persistence. The attackers modify the NetScaler configuration to map legitimate-looking file extensions—such as .ico (icon files)—to the malicious .sig PHP scripts. By placing these files in directories like /vpn/media/, the attackers create a scenario where a standard GET request to a static image file instead triggers the execution of the web shell.
Forensic analysis revealed that these requests often return HTTP 404 "Not Found" errors to casual observers, yet logs showed unusually high processing times and response sizes. This suggests that the web shell is intercepting the request, processing the malicious command, and then intentionally returning an error to throw off automated monitoring tools. Furthermore, the malware includes a "self-destruct" mechanism: if no commands or active sessions are detected within a 10-minute window, the tool automatically removes its port and lock files, effectively erasing its presence from the system memory.

Broader Impact and Implications for Infrastructure
The targeted nature of these attacks—impacting government, financial services, technology, education, and legal sectors—highlights the systemic risk posed by vulnerable edge appliances. NetScaler ADC and Gateway appliances are critical components of modern network architecture, often serving as the "front door" to internal corporate resources. Because these devices are internet-facing and reside outside the scope of most host-based Endpoint Detection and Response (EDR) solutions, they remain a "blind spot" in many organizational security programs.
Google’s threat intelligence division emphasized that this campaign is part of a larger trend: the weaponization of network infrastructure. By controlling the edge device, attackers bypass the need to compromise individual workstations or servers one by one. Once they have root access on a NetScaler appliance, they effectively own the entry point for the entire network, granting them the ability to intercept VPN credentials, access internal databases, and move laterally with ease.
Official Guidance and Remediation
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) and other international bodies have issued urgent warnings regarding the exploitation of CVE-2026-88772. Organizations currently operating NetScaler appliances are advised to perform the following actions:
- Immediate Patching: Ensure all NetScaler appliances are updated to the latest vendor-provided firmware that addresses CVE-2026-88772 and the related CVE-2026-88771.
- Configuration Review: Audit
httpd.confand other configuration files for unauthorized modifications, specifically looking for mappings that link image or archive file extensions to PHP execution. - Log Analysis: Scrutinize web server access logs for anomalous GET requests—specifically those that return 404 errors but show unusually high response sizes or latency.
- Credential Rotation: Assume that any administrative or user credentials processed by the appliance during the period of vulnerability have been compromised. Initiate a mandatory password reset for all affected users.
- Network Segmentation: Where possible, restrict access to the management interface of the NetScaler to specific, trusted administrative IP addresses and employ multi-factor authentication (MFA) at the network layer.
Conclusion: The Escalating Arms Race
The 2026 Citrix exploitation campaign serves as a sobering reminder of the fragility of enterprise security. As organizations continue to rely on centralized gateways to manage remote access and traffic delivery, these appliances become prime targets for sophisticated threat actors. The use of custom, modular malware like WHIPSHOT and SLAPSHOT indicates that the attackers are not merely "script kiddies," but disciplined operators capable of bypassing standard security controls.
The evolution of this campaign—from initial reconnaissance to mass exploitation in less than 24 hours—suggests that the window for remediation is shrinking. Security teams must shift toward a proactive posture, focusing on the integrity of their edge devices and assuming that perimeter defenses are no longer sufficient to guarantee safety. In the wake of this incident, the industry will likely see a renewed focus on hardware-level integrity monitoring and more rigorous auditing of the firmware that powers the world’s most critical network infrastructure. As the threat landscape grows more complex, the ability to rapidly detect and respond to these "invisible" web shells will be the defining factor in preventing the next major data breach.