U.S. Army Soldier Sentenced to 70 Months in Prison for Massive Data Extortion Campaign Targeting AT&T and Global Telecoms

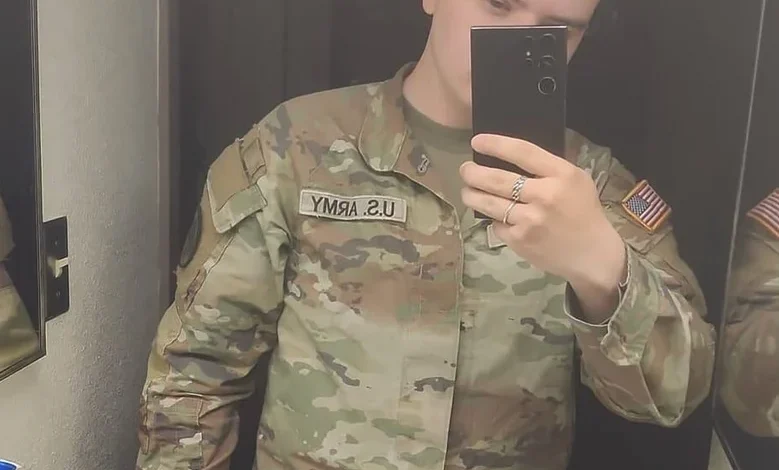
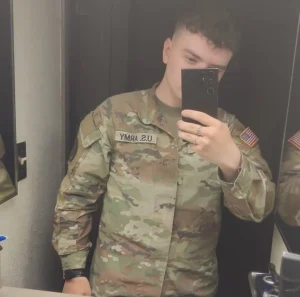
Cameron John Wagenius, a 22-year-old U.S. Army soldier formerly stationed in South Korea, has been sentenced to 70 months in federal prison following his role in a sophisticated, high-stakes cyber-extortion campaign that compromised the personal metadata of over 100 million AT&T customers. In a Seattle courtroom, federal authorities finalized a case that spanned multiple continents and triggered an urgent, multi-agency national security investigation. In addition to his prison term, Wagenius, who operated under the digital alias Kiberphant0m, was ordered to pay $294,978 in restitution to his victims.
The sentencing marks the culmination of a legal process that began in late 2025, following a collaborative investigation involving the Federal Bureau of Investigation (FBI), the U.S. Secret Service, the Army Criminal Investigative Division (CID), and the Defense Criminal Investigative Service (DCIS). While Wagenius’s actions were global in scale, the underlying infrastructure of his crimes relied on a failure of basic digital hygiene within major corporate networks.
The Anatomy of a Digital Breach
Wagenius’s campaign centered on the exploitation of unsecured credentials within the Snowflake cloud storage environment. Snowflake, a prominent cloud data platform, was targeted by Wagenius and his co-conspirators because several large corporate clients had failed to implement multi-factor authentication (MFA). By accessing these exposed accounts, the group exfiltrated massive datasets containing call and text metadata—including timestamps, durations, and source/destination phone numbers—for tens of millions of individuals.
The scope of the operation extended far beyond AT&T. Wagenius claimed responsibility for infiltrating over a dozen telecommunications firms worldwide, including Verizon’s specialized Push-to-Talk business services. Throughout 2024, he utilized cybercrime forums to taunt these corporations, threatening to release the sensitive metadata unless exorbitant ransom demands were met.
Chronology of the Criminal Enterprise
The timeline of the Kiberphant0m case highlights a rapid escalation from digital hobbyism to high-level extortion:
- 2024: Wagenius, operating from a military base in South Korea, begins his systematic exploitation of improperly secured cloud storage accounts.
- October 2024: Kiberphant0m gains notoriety on dark-web forums by publicly boasting about the theft of data from AT&T customers and initiating extortion attempts against major global telecom providers.
- November 2025: Security researcher Brian Krebs publishes findings linking the Kiberphant0m persona to a U.S. soldier based in South Korea.
- December 2025: Following the identification of his activities, Wagenius is arrested and charged under two separate federal indictments. He enters a guilty plea shortly thereafter.
- August 2026: Co-conspirator Conor Riley Moucka (alias "Judische") enters a guilty plea in Canada, further untangling the web of the criminal syndicate.
- September 2026: Federal prosecutors file a detailed sentencing memorandum noting that Wagenius attempted to probe Bureau of Prisons (BOP) network vulnerabilities while in custody.
- 2027: The sentencing hearing concludes with a 70-month prison sentence for Wagenius.
The Network of Co-Conspirators
The prosecution of Wagenius is part of a broader crackdown on a loose-knit but highly effective criminal collective. Kenneth Schuchman, a 28-year-old from Vancouver, Washington, played a pivotal role in assisting the extortion efforts. Schuchman’s involvement was particularly concerning to authorities due to his established criminal pedigree; in 2019, he pleaded guilty to operating the Satori botnet, which leveraged thousands of compromised Internet-of-Things (IoT) devices to launch massive distributed denial-of-service (DDoS) attacks.
Other figures identified in the scheme include Conor Riley Moucka, an Ontario resident who faced charges in Canada, and John Erin Binns, an American citizen currently residing in Turkey. Binns remains a person of interest in the investigation of a 2021 T-Mobile breach, which resulted in the exposure of personal data belonging to at least 76 million customers.
National Security and the Insider Threat
The case took on a distinct dimension when it was revealed that the perpetrator held a secret security clearance. Paul Russell, a resident agent in charge at the Defense Criminal Investigative Service, described the discovery of a soldier’s involvement as an "insider threat" that necessitated an immediate, all-hands-on-deck response from national intelligence and law enforcement agencies.
The threat escalated significantly when, following the arrest of Moucka and the payment of a $370,000 Bitcoin ransom by AT&T, the extortionist attempted to leverage stolen national security information. Kiberphant0m published what he claimed were internal schematics from the U.S. National Security Agency (NSA), as well as private call logs for high-profile political figures, including then President-elect Donald Trump and then Vice President Kamala Harris. This shift from corporate extortion to the trafficking of classified U.S. government intelligence transformed the case from a standard white-collar crime into a critical national security priority.
Persistent Criminal Intentions in Custody
Perhaps the most alarming aspect of the sentencing memo is the revelation that Wagenius continued his illicit research even while incarcerated. Prosecutors noted that, while awaiting his sentencing, Wagenius utilized the email accounts of other inmates to engage in "prompt injection" attacks against commercial AI models.
By framing his queries as research for a book, Wagenius attempted to bypass AI safety guardrails to extract detailed, actionable information regarding Windows 10 privilege escalation vulnerabilities and command injection techniques for D-Link networking hardware. Furthermore, he sought instructions for constructing makeshift radio antennas within the prison environment and conducted research on potential prison escape methodologies.
The government’s sentencing memorandum stated: "While Wagenius was not particularly financially successful as a cybercriminal, he both intended to and caused significant harm to numerous individual victims, U.S. companies, and the U.S. government." Records indicate that despite the millions of records exfiltrated and the high-profile extortion demands, the total profit directly attributed to Wagenius’s activities was approximately $1,500.
Broader Implications for Cybersecurity
The Kiberphant0m saga serves as a sobering case study on the vulnerabilities inherent in modern cloud infrastructure. The reliance on legacy credentials and the failure to enforce mandatory multi-factor authentication provided the initial "wedge" for an actor who was otherwise relatively unsophisticated in his financial monetization.
For corporate entities, the incident underscores the danger of "data sprawl"—the phenomenon where sensitive customer information is stored in third-party cloud environments that may not be subject to the same rigorous security auditing as core internal systems. As the digital landscape continues to evolve, the ability of a single individual—even one with limited financial success—to cause widespread, systemic disruption to global telecommunications providers remains a significant concern for regulators and national security officials.
The sentencing of Wagenius closes the chapter on a particularly disruptive period for telecom security, but the ongoing prosecutions of his co-conspirators suggest that the fight against decentralized, globalized cyber-extortion rings is far from over. The Department of Defense and federal law enforcement agencies continue to review the protocols surrounding the digital access granted to personnel with secret clearances, signaling a potential shift in how military systems are monitored for anomalous data traffic.