Google Dismantles Massive XCPE Botnet Infecting Over 1.3 Million Android TV Devices Worldwide

In a coordinated international effort, Google’s Threat Intelligence Group (GTIG) has successfully dismantled the XCPE botnet, a sophisticated network of more than 1.3 million compromised Android TV set-top boxes. The operation, which involved collaboration with various industry partners, revealed a systemic security failure within the supply chain of low-cost streaming hardware manufactured in China. By severing the command-and-control infrastructure used by the manufacturer Videostrong Technology Co., Google has effectively crippled a distribution hub that researchers estimate may have provided illicit access to as many as 10 million additional Internet of Things (IoT) devices.
The investigation exposes a troubling trend in the consumer electronics market: the intentional inclusion of malicious firmware in hardware, designed to turn innocent living room appliances into nodes for residential proxy networks and advertising fraud.
The Anatomy of the XCPE Infection
The XCPE botnet, named after a core component of the malware found within the device firmware, functioned by transforming residential internet connections into commercial assets. Once a user booted their new Android TV box for the first time, the device would automatically connect to a remote server, install the malicious payload, and begin broadcasting the user’s IP address to various "residential proxy" services.
These services operate by renting out the IP addresses of real households to third-party clients. While some legitimate use cases exist, the bulk of this traffic is frequently utilized by cybercriminals to bypass geofencing, facilitate account takeovers, conduct large-scale advertising fraud, and scrape sensitive data for the training of unauthorized artificial intelligence models.
Google’s analysis confirmed that Videostrong Technology Co. was not merely a passive manufacturer but an active participant in the monetization of these backdoors. The company reportedly sold access to these infected devices to various criminal affiliates, who used the hardware as a launchpad for additional malware modules. For the consumer, this meant that their personal network was being leveraged for malicious activity without their knowledge or consent, effectively turning their home infrastructure into a weapon against others.

A Chronology of Discovery and Takedown
The exposure of the XCPE botnet is the culmination of a year-long industry effort to map the proliferation of pre-infected IoT devices. The timeline of this issue extends back to early 2025, when researchers began noticing anomalous traffic patterns originating from cheap, "no-name" streaming boxes.
- November 2025: Security researchers at Censys and other firms began documenting how popular streaming devices, such as the Superbox, were arriving at consumers’ doors with pre-installed proxy software.
- January 2026: The startup Synthient published a landmark report on the Kimwolf botnet, which utilized similar proxy-based vulnerabilities to hammer global networks with record-breaking Distributed Denial of Service (DDoS) attacks.
- July 2026: The FBI, in a significant victory for digital security, seized hundreds of domains associated with NetNut—a subsidiary of the Israeli firm Alarum Technologies—citing the company’s involvement in the "Popa" botnet, which also targeted Android TV boxes.
- October 2026: Oxylabs, a major player in the proxy space, underwent a rebranding to "Source" following a $130 million capital infusion. The firm was later named in the GTIG report as a provider whose software development kits were frequently found on XCPE-infected hardware.
- November 2026: Google officially announced the successful disruption of the XCPE infrastructure, following deep-dive analysis by GTIG and external partners like Synthient, which identified that the malware was not limited to TV boxes but had spread to telehealth devices and industrial signage.
The Role of Supply Chain Vulnerabilities
The ease with which these devices were compromised highlights a structural vulnerability in the Android ecosystem. While Google maintains rigorous compatibility and security standards for Android TV, manufacturers like Videostrong were able to circumvent these protocols by injecting malicious code at the firmware level immediately upon the device’s initial boot sequence.
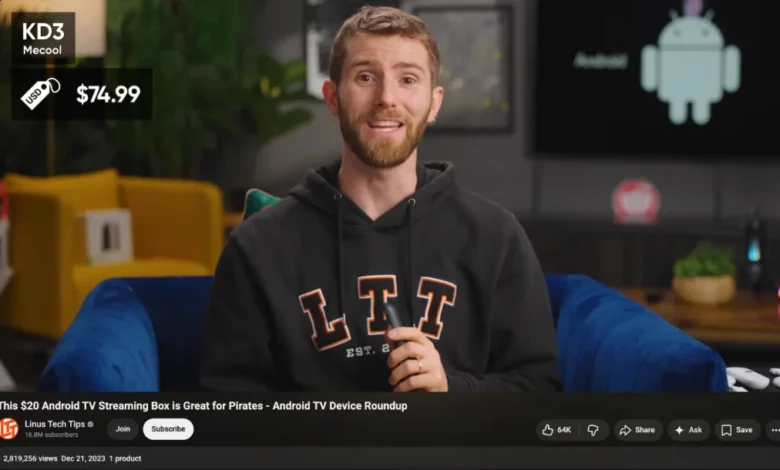
This "zero-day" delivery method meant that even devices marketed as "secure" were compromised before they ever reached the end user. Furthermore, the popularity of these devices was fueled by influencer marketing campaigns on platforms like TikTok and YouTube. In one notable instance, the YouTube channel Linus Tech Tips promoted the MECOOL streaming box—a device later identified by Synthient as being bundled with Videostrong’s malicious software. Following the revelation, the channel updated its content to classify the device as a scam and removed all associated affiliate links, illustrating the role of social media in the rapid adoption of compromised hardware.
Broader Implications for the IoT Market
The implications of the XCPE takedown are significant. By targeting the source—the manufacturer’s control servers—Google has managed to fragment a network that had become a cornerstone for several residential proxy providers. However, industry analysts remain cautious.
Ben Brundage, founder of Synthient, has stated that the 1.3 million figure is "highly conservative." Because the various criminal affiliates associated with Videostrong operate diversified distribution channels, the malware may persist on devices that were not connected to the primary control domains seized by Google.
The incident serves as a wake-up call for both consumers and regulators. For consumers, the allure of "one-time fee" streaming boxes that promise access to thousands of premium channels is often a gateway to becoming an unwitting participant in a global botnet. These devices are frequently marketed through channels that rely on the piracy of copyrighted material, making the inclusion of malware a natural extension of the manufacturer’s illicit business model.

For the proxy industry, the scrutiny from the FBI, Google, and independent research labs like Synthient marks a period of forced consolidation and accountability. As more companies find their infrastructure linked to the botnets of the day, the reputational and legal risks of operating in the "gray market" of residential proxies are becoming increasingly unsustainable.
Moving Forward: Securing the Ecosystem
Google has stated that it has since addressed the specific firmware vulnerability that allowed Videostrong to inject the malware. However, the legacy of these devices remains. Millions of units are currently in circulation, sitting in living rooms and offices worldwide.
The company is encouraging users to be wary of unverified hardware. The security of the IoT ecosystem depends on the integrity of the entire supply chain, from the chipset manufacturer to the software developer. When a manufacturer intentionally compromises the security of their own product for financial gain, the breach of trust is absolute.
As the digital landscape evolves, the intersection of piracy, IoT, and proxy networks will likely remain a focal point for security professionals. The dismantling of the XCPE botnet is a tactical victory, but it highlights a persistent strategic challenge: how to protect a global network of billions of devices when the manufacturers themselves are the primary threat actors.
For now, the disruption of the XCPE network serves as a warning to the industry. The era of "blind trust" in inexpensive, imported smart devices is coming to a close, replaced by a new focus on supply chain transparency and rigorous, independent security auditing. Consumers are urged to check the model numbers of their Android-based streaming equipment against the lists provided by security research organizations and to prioritize hardware from manufacturers with transparent security policies and established reputations. The battle against botnets is not a one-time event, but a continuous effort to ensure that the devices that power our homes do not turn against us.