Profile of Bruce Schneier: Bridging the Gap Between Technology, Security, and Public Interest

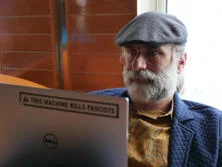
The landscape of modern cybersecurity is defined not merely by lines of malicious code or sophisticated firewalls, but by the complex interplay between human behavior, corporate governance, and societal values. At the forefront of this multidisciplinary domain stands Bruce Schneier, a towering figure whose career spans more than three decades of cryptographic research, security architecture design, and public policy advocacy. Operating at the volatile intersection of technology and human society, Schneier has cemented his reputation as one of the world’s most influential public-interest technologists, translating the arcane mathematics of encryption and network defense into accessible insights for policymakers, academics, and the general public alike.
Main Facts and Professional Scope
Bruce Schneier’s current professional footprint extends across academia, civil liberties advocacy, and private-sector enterprise architecture. He serves as a fellow and lecturer at the Harvard Kennedy School, where he helps shape the minds of future government leaders and policy architects regarding the nuances of digital security and governance. Simultaneously, he holds an academic appointment at the Munk School of Global Affairs and Public Policy at the University of Toronto, further expanding his international educational reach.
In the private sector, Schneier applies his theoretical frameworks to practical engineering as the Chief of Security Architecture at Inrupt, Inc., a technology company founded by World Wide Web inventor Sir Tim Berners-Lee. Inrupt aims to decentralize the web and restore data ownership to individuals through the Solid protocol—a mission that aligns closely with Schneier’s lifelong advocacy for digital privacy and user empowerment. Furthermore, he contributes to the safeguarding of digital civil liberties through his service on the Board of Directors of the Electronic Frontier Foundation (EFF), a premier digital rights advocacy organization. Despite these high-profile affiliations, Schneier maintains a strict editorial boundary; his personal web presence and long-running publications explicitly reflect his own independent views, distinct from the official stances of Harvard, the University of Toronto, Inrupt, or the EFF.
Chronology and Evolution of a Security Career
To understand the trajectory of Bruce Schneier’s influence, one must examine the chronological development of his contributions to the information security sector, which parallel the commercialization and expansion of the internet itself.
The early phase of Schneier’s career was characterized by foundational cryptographic research and vulnerability analysis. In the 1990s, as the internet transitioned from an academic network to a commercial infrastructure, Schneier emerged as a prolific author and cryptographer. In 1993, he designed the Blowfish symmetric block cipher, followed by the Twofish cipher in 1998, both of which became widely adopted standards for data encryption. During this decade, he also published seminal texts, including "Applied Cryptography" in 1994, which became the definitive manual for software developers and security engineers seeking to implement cryptographic protocols.
Recognizing that cryptographic algorithms alone could not secure complex socio-technical systems, Schneier expanded his focus toward broader systems security and risk management. In 1998, he launched Crypto-Gram, a monthly electronic newsletter dedicated to security, cryptography, and digital privacy. Crypto-Gram quickly grew into an essential industry resource, read by hundreds of thousands of technologists, journalists, and government officials.
As the digital age matured into the 2000s, Schneier formally established his public-facing digital presence by launching his eponymous security blog in 2004. This platform allowed him to provide real-time commentary on emerging cyber threats, government surveillance programs, and corporate data practices. Throughout the 2010s, following the 2013 disclosures by Edward Snowden regarding global mass surveillance, Schneier played a vital role in interpreting complex intelligence agency capabilities for the public, advocating robust end-to-end encryption, and warning against the dangers of government-mandated surveillance backdoors. In recent years, his focus has shifted toward the systemic risks posed by artificial intelligence, automated decision-making systems, and the urgent need to conceptualize cybersecurity as a public good rather than a mere private commodity.
Supporting Data and Publications
Schneier’s extensive body of written work provides a quantitative baseline for his impact on the cybersecurity discourse. Over a career spanning more than 30 years, he has authored or co-authored over a dozen books, covering topics ranging from national security and intelligence policy to the psychology of human fear and risk perception. His notable publications include "Data and Goliath: The Hidden Battles to Collect Your Data and Control Your World" (2015) and "Click Here to Kill Everybody: Security and Survival in a Hyper-Connected World" (2018).
His monthly newsletter, Crypto-Gram, has maintained continuous publication for over a quarter of a century, representing one of the longest-running continuous commentary channels on digital security in existence. Academically, his research papers and articles have been cited tens of thousands of times across computer science and public policy literature. His conceptualizations of security paradigms—such as the balance between security, convenience, and privacy—form foundational case studies in university computer science and political science curricula worldwide.
Official Responses and Institutional Impact
While Schneier’s writings often critique institutional overreach, corporate negligence, and government policy failures, his expertise is regularly sought by official bodies, legislative committees, and academic institutions. Over the years, he has testified before United States congressional committees on cybersecurity infrastructure, encryption policy, and the regulatory challenges of emerging technologies.
Academic institutions have consistently integrated his frameworks into their research centers. At the Harvard Kennedy School and the Munk School, his lectures bridge the traditional divide between hard engineering disciplines and soft public policy domains. Colleagues and institutional leaders frequently praise his ability to articulate the societal stakes of technical decisions. In digital rights circles, the Electronic Frontier Foundation routinely highlights his board leadership and analytical clarity as instrumental in guiding civil society’s response to overreaching surveillance legislation. Conversely, intelligence and law enforcement agencies have at times clashed with his staunch defense of uncompromised encryption, reflecting the ongoing societal tension between public safety mandates and individual privacy rights.
Broader Impact and Implications for the Future
The implications of Bruce Schneier’s work extend far beyond individual software vulnerabilities or corporate data breaches; they strike at the heart of how democratic societies govern digital infrastructure. As the world transitions deeper into an era defined by the Internet of Things (IoT), autonomous systems, and generative artificial intelligence, the vulnerabilities he has highlighted for decades are manifesting at a systemic scale.
Schneier has consistently argued that market forces alone are insufficient to secure the digital ecosystem. Because software vendors face economic incentives to prioritize speed-to-market over robust security architecture, critical infrastructure remains inherently fragile. His advocacy for "public-interest technology"—an interdisciplinary field that applies technological expertise to solve societal challenges—seeks to correct this market failure by training professionals who view software and hardware not merely as commercial commodities, but as critical public infrastructure that demands rigorous regulatory oversight and ethical stewardship.
Furthermore, Schneier’s analysis of artificial intelligence governance underscores the impending risks of automated warfare, algorithmic bias, and automated cyberattacks operating at machine speed. As human operators are increasingly removed from real-time defense loops, the demand for resilient, verifiable, and human-centric security architectures becomes paramount. By maintaining a relentless focus on the intersection of technology and humanity, Bruce Schneier continues to serve as an indispensable voice, challenging policymakers, technologists, and citizens to confront the complex realities of a hyper-connected world before the security of digital society outpaces its capacity to govern itself.