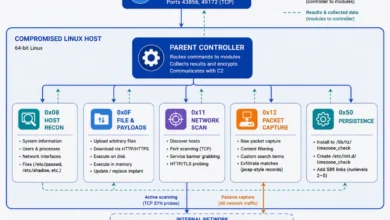
The cybersecurity landscape is currently undergoing a seismic shift as the emergence of "Mythos-class" artificial intelligence tools drastically reduces the time between a vulnerability’s public disclosure and the weaponization of that flaw. Historically, security teams operated under the assumption that they possessed a window of days or even weeks to patch critical vulnerabilities after a Common Vulnerabilities and Exposures (CVE) identifier was assigned. Today, that luxury of time has vanished. Advanced AI models, capable of automating the creation of exploits and identifying targetable surfaces at machine speed, have turned the traditional, manual vulnerability management lifecycle into an obsolete framework.
The Erosion of the Patching Window
For over two decades, the industry standard for vulnerability management has relied heavily on the Common Vulnerability Scoring System (CVSS). Security operations centers (SOCs) typically ingest these scores, prioritize them based on numerical severity, and allocate resources to patch the most critical items during periodic maintenance windows—often scheduled on a weekly or quarterly basis. This strategy, while orderly, fails to account for the speed at which modern threat actors move.
The term "Mythos-class" refers to a new generation of automated threat intelligence and exploitation frameworks. These systems leverage large language models (LLMs) and advanced heuristic analysis to ingest raw CVE data, cross-reference it with known software configurations, and generate functional exploit chains within minutes. When the time to exploit drops to near zero, a quarterly patching cycle becomes an open invitation for a data breach. The risk gap is no longer defined by the absence of a patch, but by the delay in validating whether a specific environment is truly susceptible to a real-world attack.
Chronology of a Vulnerability Lifecycle
The traditional workflow begins with the publication of a CVE in the National Vulnerability Database (NVD). In the pre-AI era, the timeline looked like this:
- Day 0: Vulnerability disclosure.
- Days 1–3: Security teams scan their inventory to identify affected assets.
- Days 4–10: IT operations perform risk assessment and staging.
- Days 14–30: Patch deployment and testing.
In the current environment, the "Mythos-class" threat compresses this significantly:
- Minute 0: CVE disclosure hits the public domain.
- Minute 5: Automated AI crawlers identify the vulnerability and cross-reference it with common enterprise software.
- Minute 30: Weaponized exploit code is generated and pushed to automated botnets.
- Minute 60: Active scanning and exploitation attempts begin against global internet-facing infrastructure.
This temporal disparity creates a fundamental disconnect. If a security team takes three weeks to validate a risk that an adversary can weaponize in three hours, the organization is effectively operating without a security perimeter.
Moving Beyond Severity Scores
The reliance on CVSS scores alone has long been criticized by industry experts as a flawed metric for risk. A CVSS score provides a theoretical measure of a vulnerability’s potential impact, but it does not account for the compensatory controls, network architecture, or specific configurations of a target environment.
For instance, a vulnerability may receive a "Critical" 9.8 score because it allows for remote code execution. However, if that service is hidden behind a strictly configured Web Application Firewall (WAF) or is not accessible from the public internet, the practical risk to the organization is negligible. Conversely, a "Medium" severity vulnerability—often ignored by busy patching teams—might serve as the perfect initial access vector for an attacker who has already breached the perimeter via social engineering.

Modern security practitioners are shifting toward "risk-based vulnerability management" (RBVM). This approach requires shifting the focus from the vulnerability itself to the exploitability of the environment. Validation is the key; teams must be able to prove, through controlled simulations, that an exploit will actually trigger the intended malicious behavior within their specific software and network stack.
The Challenge of Production Testing
One of the most significant hurdles in adopting a validation-first mindset is the fear of disrupting production systems. Organizations are often hesitant to run active exploit code against sensitive databases or mission-critical servers, fearing that the testing process itself could lead to downtime or data corruption.
This is where behavioral mapping and breach and attack simulation (BAS) technologies enter the narrative. Instead of running a "live" exploit that might crash a system, security teams can now map the attack techniques associated with a CVE to specific security controls. By simulating the "behavioral footprint" of an exploit—such as the specific API calls, network traffic patterns, or unauthorized process executions—security teams can determine if their existing controls, such as Endpoint Detection and Response (EDR) or Intrusion Prevention Systems (IPS), are capable of identifying and blocking the threat.
This method provides empirical evidence of readiness without the risks associated with executing raw exploit code. It replaces the assumption that "we are patched" with the verified knowledge that "our controls are active and effective."
Industry Perspectives and Expert Guidance
Industry experts, such as Ishak Celikkanat, the Solutions Architect Lead at Picus Security, argue that the goal of the modern SOC should be the creation of a "continuous validation loop." During recent industry briefings, experts have emphasized that if an environment can change within minutes due to software updates or cloud configuration shifts, the validation process cannot remain a static, periodic event.
The implications of this shift are profound for Chief Information Security Officers (CISOs). Budgetary allocations are increasingly moving away from purely preventative tools toward platforms that provide continuous visibility into the efficacy of the entire security stack. The question is no longer "what vulnerabilities do we have?" but "can we prove that our current security posture is sufficient to stop an automated, AI-driven adversary?"
The Future of Vulnerability Management
As we look toward the remainder of the decade, the integration of generative AI into the threat landscape is inevitable. The "Mythos-class" era represents a permanent change in the threat model. Organizations that fail to adapt their workflows to meet the velocity of automated attacks will find themselves in a state of perpetual catch-up.
To remain resilient, organizations must adopt three core principles:
- Automation of Validation: Move away from manual scanning and toward automated, continuous breach simulation.
- Contextual Prioritization: Ignore the static CVSS score in favor of risk metrics that include environmental context and the availability of exploit code.
- Behavioral Defense: Focus on detecting the techniques and tactics (TTPs) associated with exploits rather than waiting for specific CVE signatures, which are often easily bypassed by obfuscated, AI-generated code.
The gap between disclosure and exploitation is the primary battlefield of modern cybersecurity. While the technical sophistication of attackers continues to rise, the ability to rapidly validate security controls remains the most effective weapon in the defender’s arsenal. By proving readiness through simulation, organizations can move from a state of reactive anxiety to proactive, defensible security.