New Brazilian Banking Malware Campaign KREMLIN Leverages Blockchain Infrastructure to Evade Detection

Cybersecurity researchers have uncovered a sophisticated, multi-stage banking malware operation targeting financial institutions across Brazil. The campaign, identified by Elastic Security Labs as REF9334, has been active since at least May 2025 and utilizes a modular toolkit dubbed KREMLIN. This operation is notable for its tactical integration of blockchain technology to obfuscate command-and-control (C2) infrastructure, a move that significantly complicates traditional takedown efforts by law enforcement and security vendors.
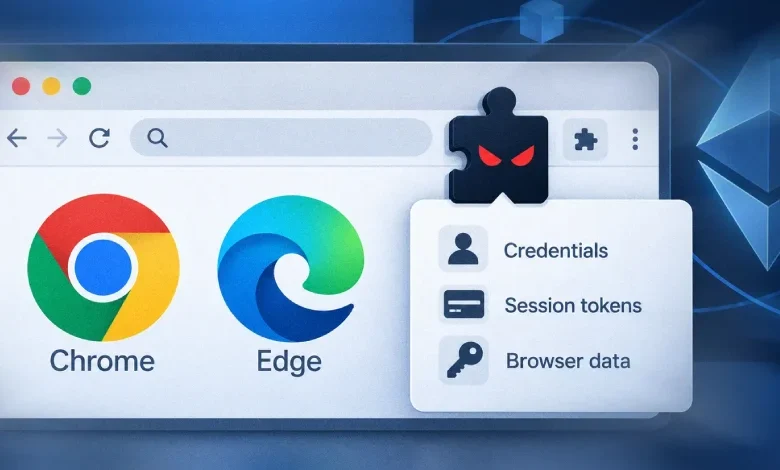
The KREMLIN ecosystem is a highly engineered threat that moves beyond simple credential theft. It employs a complex array of JavaScript loaders, custom C++ installers, and malicious browser extensions designed to hijack user sessions and exfiltrate sensitive financial data from Google Chrome and Microsoft Edge browsers. By manipulating Chromium’s internal integrity mechanisms, the threat actors have successfully bypassed standard security protocols that typically prevent the unauthorized installation of browser-based surveillance tools.
Chronology and Operational Timeline
The activity associated with REF9334 traces back to early 2025, though the group’s infrastructure underwent a significant evolution on May 19, 2026, when it began incorporating Ethereum smart contracts as dead drop resolvers. This transition marked a strategic shift toward decentralization, allowing the operators to dynamically update their C2 endpoints and payload hosting locations without relying on traditional, easily sinkholed domain name systems.
Since June 16, 2025, security researchers have attributed seven distinct campaigns to this threat actor. These campaigns have consistently focused on the Brazilian banking sector, utilizing lures that impersonate legitimate financial correspondence, invoices, or corporate documentation. The progression of the malware’s capabilities—from standard trojans like Pulsar and Remcos to the highly specialized KREMLIN toolkit—reflects an adversary that is both well-funded and technically proficient.

Technical Architecture and Evasion Tactics
The KREMLIN infection chain begins with a user manually executing a deceptive JavaScript file. This initial stage serves as a gatekeeper; it performs rigorous environmental checks to ensure it is not running within a sandboxed environment or a virtual machine. If the malware detects virtualization, it terminates immediately to avoid analysis.
The second stage of the infection is where the architectural complexity becomes apparent. Upon establishing persistence through scheduled tasks, the malware queries an Ethereum smart contract—specifically located at the address 0xCD7360A83E5cdbBbbbcEB0e78748babA6740d07b—to retrieve updated download locations. This "dead drop" mechanism acts as a bridge, directing the malware to the appropriate servers to fetch the third-stage C++ installer.
The installer itself employs a technique known as DLL sideloading, abusing a legitimate SentinelOne binary to execute an unsigned payload disguised as "SentinelAgentCore.dll." This component performs further system-level reconnaissance, checking for CPU core counts and RAM capacity to verify that it is running on a genuine victim’s machine rather than an automated analysis platform. If the system specifications do not meet the attacker’s threshold, the process halts, effectively shielding the malware from most automated security scanners.
The Phantom Extension and Browser Hijacking
Once the environment is deemed suitable, the KREMLIN toolkit deploys a malicious browser extension. The operators utilize a technique known as "Phantom Extension" to bypass Chromium’s Secure Preferences. By modifying the browser’s JSON configuration files and regenerating the required HMAC and App-Bound encrypted hashes, the attackers inject their extension—masquerading as "AVSync System Inc."—without alerting the user or the browser’s internal integrity checkers.
This methodology mirrors sophisticated tactics previously observed in global espionage campaigns, such as the August 2026 campaign linked to the China-based APT31 group, which used the BlueMoon exploit kit to deploy the GemStone extension. The convergence of these techniques suggests a broader trend where threat actors are increasingly prioritizing the browser as the primary vector for persistent data theft.

Once installed, the KREMLIN extension requests extensive permissions, including full access to browser tabs, cookies, and local storage. It establishes a persistent WebSocket connection to its C2 server, identified as "luizestrelhashapr[.]online," allowing the attackers to execute arbitrary commands, intercept web requests, and scrape session tokens in real-time.
Network Canary and Defensive Implications
One of the most revealing aspects of the Elastic Security Labs investigation was the discovery of a "network canary" mechanism. The malware attempts to download a page from an unregistered domain to verify its connection. If it receives a valid response—often a result of a security vendor or sandbox simulating a network connection—the malware triggers a self-destruct sequence.
By registering this canary domain, Elastic researchers were able to monitor the scale of the operation, identifying at least 1,515 infected systems. The geographical concentration is stark, with over 98% of the identified infections located within Brazil. While the researchers noted that their intervention temporarily degraded the malware’s defense mechanisms, the sheer volume of infected endpoints highlights the persistent risk posed by this operation.
Broader Impact and Industry Analysis
The KREMLIN campaign underscores a critical evolution in the threat landscape: the fusion of financial cybercrime with advanced persistent threat (APT) methodologies. The use of blockchain to hide infrastructure is not merely a technical novelty; it represents a significant challenge to the traditional "follow the money" and "sinkhole the domain" approaches used by cybersecurity firms and law enforcement agencies.
Financial institutions in Brazil are facing an increasingly complex threat environment. The reliance on browser-based attacks suggests that these actors are bypassing traditional antivirus software by focusing on the application layer. Furthermore, the use of stolen or forged metadata to authenticate malicious extensions indicates a need for more robust browser-side validation processes by major technology providers.

"The move to decentralized C2 infrastructure via smart contracts is a game-changer for threat actors," says a senior security analyst. "It forces defenders to shift from reactive infrastructure blocking to proactive, behavioral-based detection. Organizations can no longer rely on simple blacklists when the underlying infrastructure can be rotated at the speed of a blockchain transaction."
Recommendations for Mitigation
Security professionals and financial institutions are urged to adopt a multi-layered defense strategy to combat KREMLIN:
- Endpoint Monitoring: Organizations should monitor for unauthorized modifications to browser Secure Preferences and the suspicious installation of browser extensions, particularly those with excessive permission requirements.
- Process Whitelisting: Implementing strict application control policies to prevent the execution of unsigned binaries or the sideloading of DLLs, especially those that attempt to mimic security software like SentinelOne.
- Network Visibility: Security teams should investigate internal traffic patterns for unusual WebSocket connections and attempts to resolve obscure or newly registered domains that may be linked to blockchain-based C2 redirects.
- User Education: Given the reliance on deceptive documents and invoice lures, continuous employee training remains essential to prevent the initial execution of the malicious JavaScript loaders.
The KREMLIN operation serves as a sobering reminder that the barrier to entry for highly sophisticated cyberattacks is dropping. As actors continue to refine their methods for evading sandbox detection and leveraging decentralized technologies, the need for international cooperation and advanced threat intelligence sharing becomes paramount to protecting the global financial ecosystem. The investigation into REF9334 remains ongoing, and as further details emerge, it is likely that the industry will see a heightened focus on the security of browser-based environments and the integrity of the Chromium platform.
Related posts: