Critical Linux Kernel Vulnerability CVE-2026-98432 Exposes Servers to Remote Root Compromise

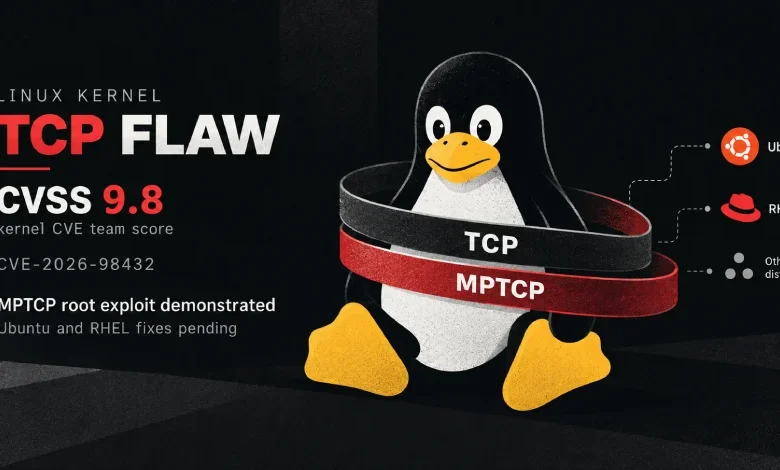
A severe security vulnerability, identified as CVE-2026-98432, has sent shockwaves through the enterprise Linux ecosystem. This critical flaw resides within the Linux kernel’s TCP networking stack, specifically impacting the handling of IPv4 connections. With a CVSS score of 9.8 out of 10 assigned by the kernel’s own security team, the vulnerability represents a significant risk, potentially allowing unauthenticated remote attackers to execute arbitrary code with root-level privileges on affected servers.
The flaw is rooted in a race condition occurring during the initial stages of a TCP handshake. When the kernel processes new connection requests, it fails to properly manage the lifecycle of memory associated with IP options. Specifically, the kernel transfers IP options from a pending connection request to a newly established socket without creating a distinct copy. If the socket is subsequently terminated while another CPU core is still attempting to access those original options—often in response to a retransmitted connection request—the system triggers a "use-after-free" condition. This allows an attacker to manipulate kernel memory, potentially leading to unauthorized data disclosure or full system compromise.
The Role of AI in Vulnerability Research
The discovery of this exploit has brought the intersection of Artificial Intelligence and cybersecurity into sharp focus. On October 27, 2026, researchers at Anthropic disclosed that their advanced AI model, Claude, was instrumental in developing a functional exploit for this specific kernel vulnerability. According to the disclosure, the AI model successfully drafted the exploit code after receiving initial prompts from researchers, demonstrating the potential for LLMs to accelerate the weaponization of software flaws.
The exploit designed by the AI operates in two distinct phases. First, it leverages the race condition to leak sensitive kernel memory, effectively bypassing Kernel Address Space Layout Randomization (KASLR). By forcing the kernel to return extra bytes during a failed connection attempt, the attacker gains the necessary memory addresses to map the kernel’s internal structure. Once KASLR is defeated, the second phase involves a buffer overflow that overwrites a callback pointer with the address of an attacker-supplied payload. When the kernel executes this pointer, it unwittingly triggers the attacker’s shell command with root permissions. Anthropic’s tests indicated that, while the process is time-consuming—requiring approximately 53 minutes to complete the full chain—it is highly reliable because failed attempts do not crash the system, allowing for continuous iteration.
Chronology of Discovery and Disclosure
The timeline of CVE-2026-98432 highlights a rapid transition from internal patch development to public disclosure.

- October 5, 2026: Kernel developers proactively apply a fix to the upstream Linux source tree to address the race condition, effectively preventing the memory management error by ensuring the kernel waits for CPU processes to conclude before freeing the associated options.
- October 15, 2026: The CVE is formally published, drawing attention to the potential risk, though it lacks specific mention of Multipath TCP (MPTCP) at this stage.
- October 16, 2026: Early adopters, including Debian and Oracle Linux, release patched kernel packages to their user bases.
- October 24, 2026: The Linux kernel security team updates the CVE record with the 9.8 CVSS score, emphasizing the potential for remote root exploitation. Amazon Linux 2023 ships its first round of fixes for specific kernel versions.
- October 27, 2026: Anthropic publishes its report on the AI-generated exploit, explicitly linking the vulnerability to servers utilizing Multipath TCP listeners.
- October 29, 2026: Major enterprise distributions, including Ubuntu and Red Hat Enterprise Linux (RHEL), remain in the process of developing or testing their respective patches, leading to widespread concern among system administrators.
Divergent Severity Assessments and Industry Response
The security community has observed a notable discrepancy in how different vendors perceive the threat level of CVE-2026-98432. While the Linux kernel team maintains a critical 9.8 score, vendors like Red Hat initially characterized the flaw as "Moderate" with a 5.9 score. This variance stems from differing assumptions regarding "exploitability."
Red Hat’s lower score reflected the difficulty of successfully winning a race condition in a real-world, high-traffic environment. However, as the implications of the AI-generated exploit became clearer, sentiment shifted. By late October, Red Hat updated its advisory to "Important" with a score of 8.1, acknowledging that while the race is difficult to win, the integrity and confidentiality impacts are severe if achieved. Other vendors, including SUSE and Oracle, aligned with this 8.1 assessment, focusing on the high-complexity, high-impact nature of the flaw.
This lack of consensus creates a complex landscape for security operations teams. While organizations running Debian or Oracle Linux have clear remediation paths, those relying on RHEL or Ubuntu are currently in a "wait-and-see" position, relying on the hope that vendor-specific mitigations will be released shortly.
Technical Implications and Mitigation Strategies
The vulnerability specifically targets the IPv4 stack; IPv6 is notably immune because the kernel correctly copies connection options in that protocol. The risk is significantly amplified for servers running MPTCP, a protocol that allows a single connection to utilize multiple network paths. MPTCP must be explicitly requested by an application, which means that standard web servers or databases not configured to use this feature may have a lower surface area for attack, though the full extent of the risk remains subject to ongoing analysis.
For system administrators, the primary recommendation remains the same: monitor vendor security advisories and apply patches as soon as they become available. For organizations that build custom kernels, the upstream fix is integrated into stable versions including 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.56, 7.2.10, and 7.3. The kernel development community explicitly advises against "cherry-picking" individual patches, instead recommending an upgrade to the latest supported stable release to ensure all dependent security fixes are included.
There are currently no widely accepted, universal workarounds. While some security professionals have suggested disabling MPTCP, there is no official documentation confirming that this provides a complete defense against the exploit. Similarly, blocking incoming connection requests that carry specific IP options has been suggested, but such measures risk disrupting legitimate network traffic and are generally not recommended as a substitute for patching.

Broader Impact on Cybersecurity Governance
The involvement of Anthropic in exposing this vulnerability highlights a significant shift in how vulnerabilities are discovered. Historically, kernel bugs were found through manual code audit or fuzzing tools. The ability of an LLM to not only identify the bug but also construct a multi-stage exploit chain suggests that the "time-to-exploit" window for new vulnerabilities is shrinking.
This development poses a challenge for software supply chain security. If AI can generate exploits for critical infrastructure at scale, the reliance on reactive patching cycles may no longer be sufficient. Security teams must now consider the possibility that attackers are using similar AI tools to discover and weaponize flaws in proprietary and open-source software before defenders have even identified the vulnerability.
Furthermore, the delay in patch availability for major enterprise distributions underscores the fragility of the open-source software ecosystem. When critical bugs are found in the Linux kernel, the "last mile" of delivery—the process of getting the fix into the hands of users via distributions—remains a bottleneck. This period of exposure, where a vulnerability is public but unpatched for specific systems, is the most dangerous window for data breaches.
As organizations navigate the fallout of CVE-2026-98432, the focus will likely turn toward proactive hardening and the adoption of more agile patch management workflows. With the threat landscape increasingly populated by automated and AI-driven attack vectors, the industry’s ability to coordinate, communicate, and remediate will be tested more than ever before. For now, the most critical step for the enterprise community is to maintain strict vigilance over security bulletins from Red Hat, Ubuntu, and other major Linux vendors, ensuring that as soon as the definitive patches arrive, they are deployed across all affected server infrastructure.